
Overview
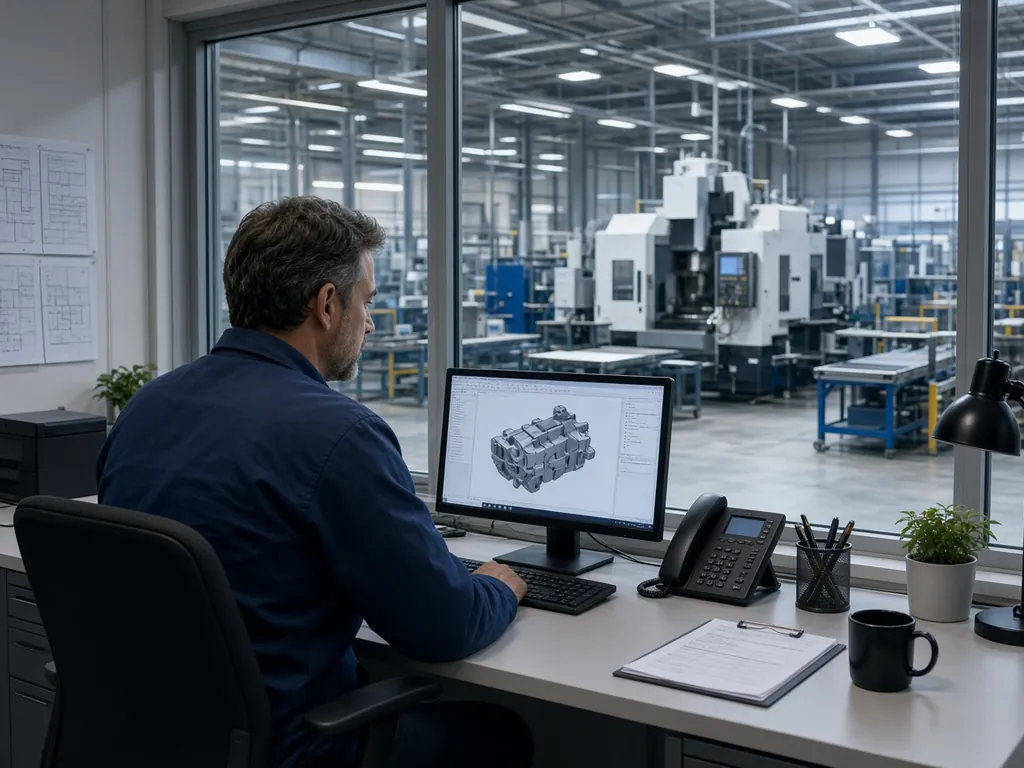
Manufacturers often combine modern office IT with older production equipment that cannot be patched as easily. Keeping those networks separate and monitored reduces the chance that a phishing email in the office turns into a stopped production line.
For defense-supply-chain businesses, CMMC has added specific cybersecurity expectations. Phase II requirements were suspended in July 2026 pending review, while Phase I self-assessment requirements remain in place, so check the DoD CIO CMMC page for current status.
Common IT challenges
- ERP and production systems that cannot go down
- Older shop-floor PCs and controllers that cannot easily be patched
- Defense contractors facing CMMC self-assessment requirements (Phase II was suspended in July 2026; check current status)
- Multiple sites and shifts
How we help
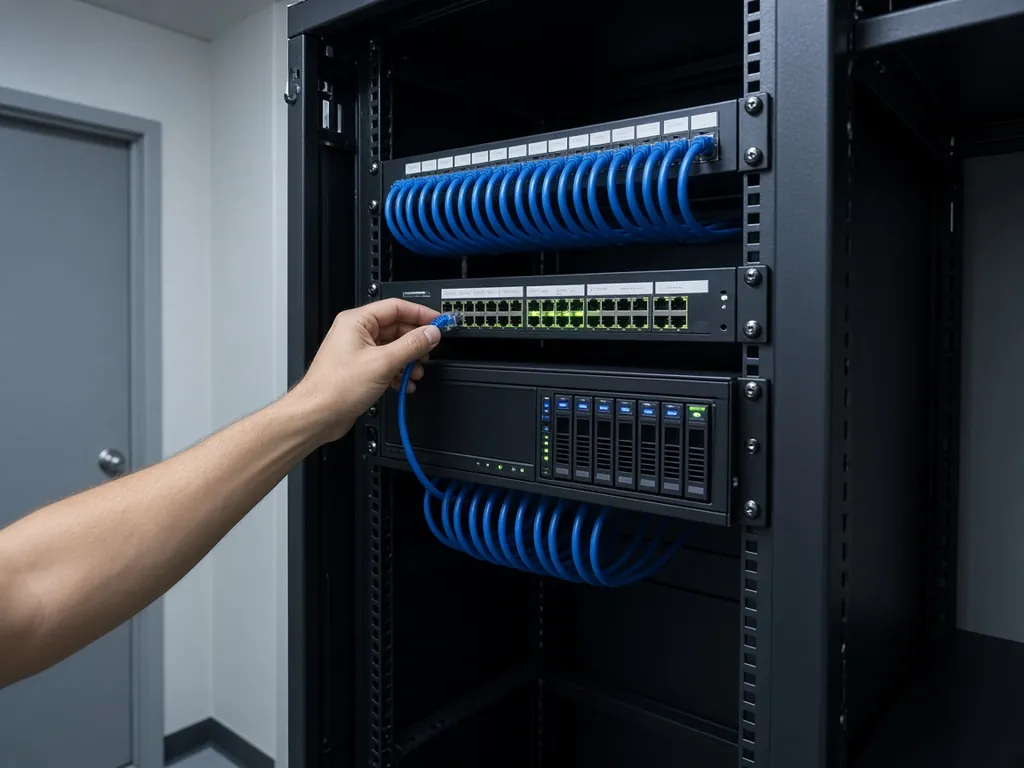
- Network segmentation between office IT and shop-floor systems
- Monitoring and planned maintenance windows
- Backups and recovery plans for ERP
- CMMC readiness gap assessment support
- After-hours support aligned to shifts
Key services for this sector
 ServiceNetwork & Wi-FiReliable, secure office networks: firewalls, switches, Wi-Fi and guest access designed properly.Learn more →
 ServiceCompliance supportTechnical controls and documentation for HIPAA, the FTC Safeguards Rule, PCI DSS and CMMC readiness.Learn more →
 ServiceBackup & disaster recoveryTested backups of servers, laptops and Microsoft 365, with a recovery plan you can actually follow.Learn more →
Frequently asked questions
Can you work around our production schedule?
Yes. Maintenance and changes can be scheduled for planned downtime or between shifts.
Do you support our ERP?
We support the servers, network, devices and backups behind it, and coordinate with the ERP vendor.
Can you help with CMMC?
We can support a readiness gap assessment and implement technical controls. Certification itself is handled by authorised assessors.